NDR
Дэлгэрэнгүй тайлбарDetailed information詳細情報Informations détailléesDetaillierte Informationen
Блокын гарчиг / html
A few years ago, we relied on firewalls and antivirus software, using known attack signatures for protection. Today, however, cyber attackers increasingly use artificial intelligence to launch zero-day attacks that have never been seen before.
In this new era of cyber competition, traditional rules- and signature-based security solutions are increasingly proving inadequate. At this critical juncture, Darktrace, a company founded through the collaboration of mathematicians from the University of Cambridge and cybersecurity experts in the United Kingdom, is setting a new standard in the security industry with its self-learning AI-powered NDR (Network Detection and Response) solution.
What is NDR (Network Detection and Response)?
NDR, or Network Detection and Response, is a cybersecurity technology designed to help organizations monitor, detect, and respond to suspicious activity across their networks. While traditional EDR (Endpoint Detection and Response) focuses primarily on endpoint devices, and SIEM analyzes logs and security event data, NDR analyzes network traffic in real time to identify suspicious behavior and enable an appropriate response.
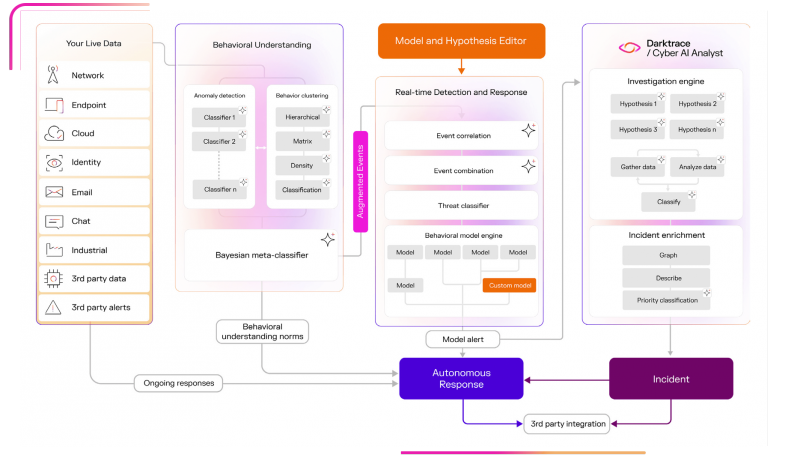
Darktrace NDR continuously learns an organization’s normal network behavior and automatically establishes a dynamic baseline, reducing reliance on manually defined rules or known attack signatures. Rather than depending solely on previously identified signatures, it can detect subtle anomalies and unusual patterns associated with sophisticated attacks, including previously unseen or zero-day threats, as well as potential insider threats originating from within the network.
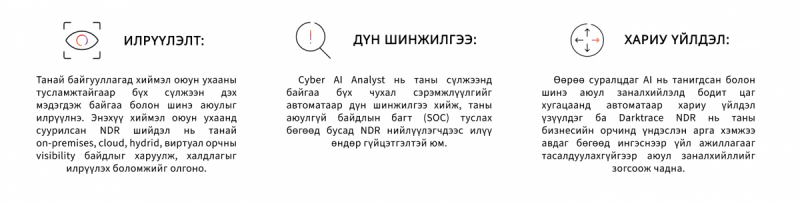
HOW DOES DARKTRACE NDR DETECT ATTACKS?
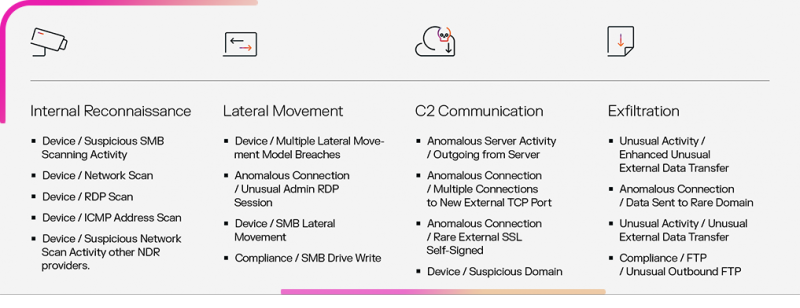
Darktrace / NETWORK provides coverage across all 14 MITRE ATT&CK tactics, enabling it to detect threats throughout the different stages of an attack without relying solely on historical data, static rules, or known signatures.
By continuously learning what is normal for the organization’s network, Darktrace / NETWORK can identify unusual behavior and emerging threats that deviate from established patterns.
Below are several examples of how Darktrace / NETWORK can detect anomalous behavior and potential threats across your network.
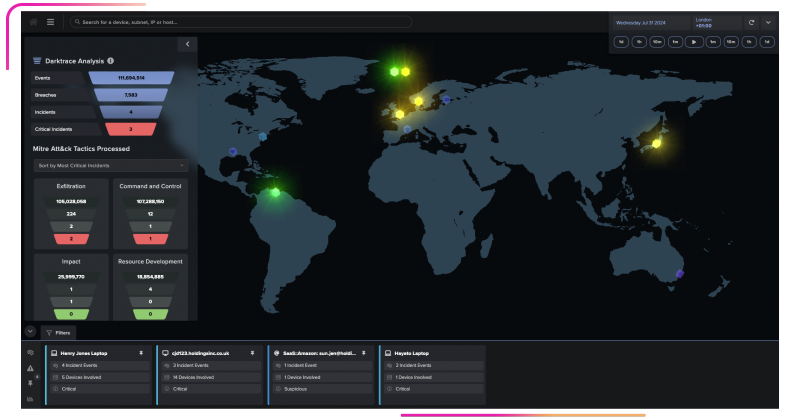
COMPLETE NETWORK VISIBILITY
Darktrace / NETWORK monitors traffic across on-premises, virtual, cloud, and hybrid environments, analyzing both encrypted and unencrypted data to detect anomalous activity in real time.
Unlike many other NDR solutions, Darktrace AI learns exclusively from your organization’s own data, allowing it to establish an understanding of normal behavior without relying on external threat intelligence or continuous cloud connectivity. This enables organizations to maintain effective network threat detection while keeping analysis closely aligned with their own environment.
DETECTS KNOWN AND UNKNOWN THREATS
Darktrace / NETWORK does not rely on historical data, malware signatures, or external threat intelligence. Instead, it continuously learns what is normal for your network and identifies deviations from that baseline.
This enables Darktrace to effectively detect a wide range of anomalous activity, including both external attacks and insider threats, as well as previously unknown or emerging threats that traditional signature-based tools may miss.
.
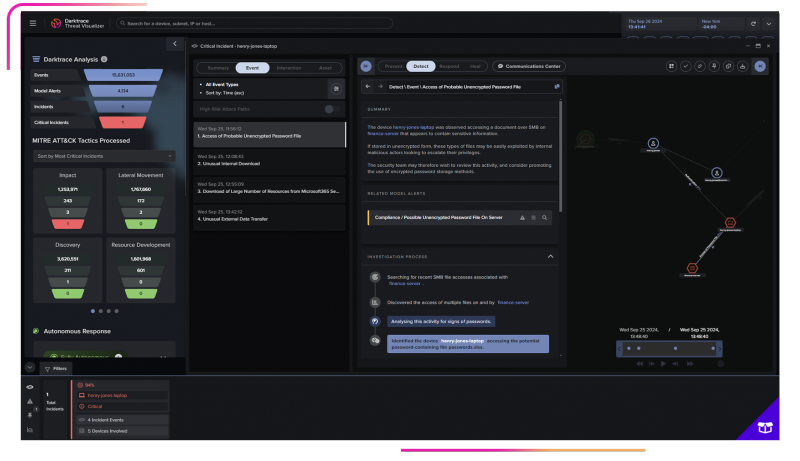
HIGH-PRECISION THREAT DETECTION
Darktrace’s AI helps reduce unnecessary alerts, quickly surfaces high-priority incidents, and minimizes false positives so security teams can focus on the threats that matter most.
Security teams can also review and fine-tune the AI’s detection logic, adjust configurations when needed, and easily create custom detection models without incurring additional costs.
Darktrace integrates with your existing technology ecosystem to help streamline threat detection, investigation, response, and operational workflows.
Darktrace / NETWORK works alongside your existing firewall, ZTNA, SIEM, SOAR, and ITSM platforms, enhancing the effectiveness of your current security infrastructure rather than replacing it. It can also integrate with leading EDR solutions such as Microsoft Defender, Check Point, and SentinelOne, combining endpoint and network-level intelligence to enable more effective threat detection, investigation, and response.
If your organization is looking to reduce cyber risk and take network security to the next level, contact us to learn more about Darktrace NDR and its broader cybersecurity solutions.
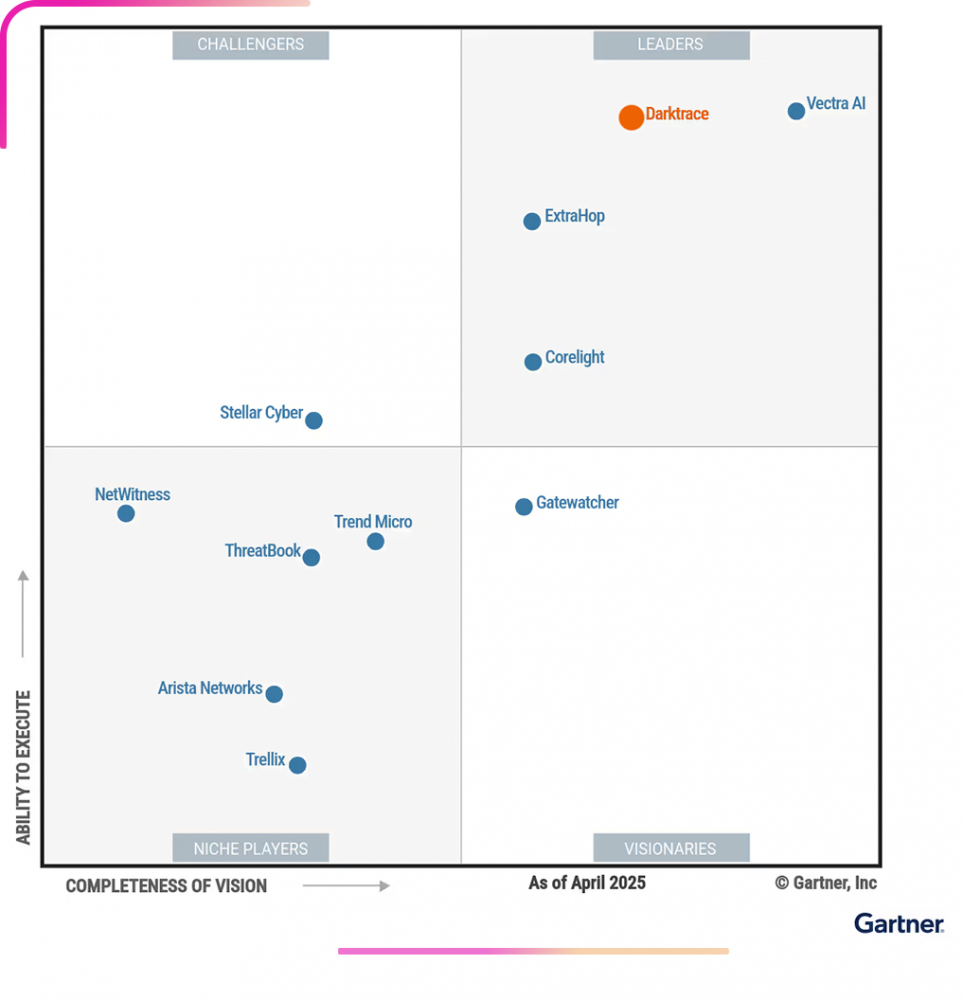
2025 Gartner® Magic Quadrant™ for "NDR"
Darktrace компани 2025 оны Gartner® Magic Quadrant™ for "Network Detection and Response (NDR)" төрөлд тэргүүлэгчээр шалгарсан төдийгүй Мөн:
IDC, & KuppingerCole зэрэг олон тайланд Тэргүүлэгчээр нэрлэгдсэн
AI-аар удирдуулсан SOC (AI-led SOC) руу шилжих замаар SOC-ийн өөрчлөлтийг хурдасгаж байна
Уламжлалт NDR-ээс давж — Сүлжээний идэвхтэй уян хатан байдлыг (proactive network resilience) бий болгосон
10,000 гаруй байгууллагууд Darktrace компанийн NDR шийдэлд аюулгүй байдлаа даатгаж байна.