NextGen SIEM Platform
Дэлгэрэнгүй тайлбарDetailed information詳細情報Informations détailléesDetaillierte Informationen
Блокын гарчиг / html
.jpg)
Security Information and Event Management (SIEM)
Has your organization invested heavily to fully protect its cybersecurity, yet still may not be adequately prepared for risk? Or are you still spending substantial time on repetitive manual work when analysis can be performed on a ready-made platform?
If so, discover the next generation of SIEM solutions. Next-generation SIEM technology goes beyond log management, using a comprehensive architecture with the capability to detect unknown attacks.
Блокын гарчиг / icon_box
Enables faster threat detection and response than ever before.
When stopping an attack, every second counts. It rapidly identifies threats, filters log data efficiently, supports confident decision-making, and helps remediate incidents without delay.
Achieves more with the resources you already have.
Your team can focus on other critical priorities without having to worry about ongoing SIEM development and maintenance.
Faster threat detection and response than ever before.
As your organization’s data continues to grow rapidly, it maintains high performance even at scale while helping reduce overall operational costs.
Блокын гарчиг / html
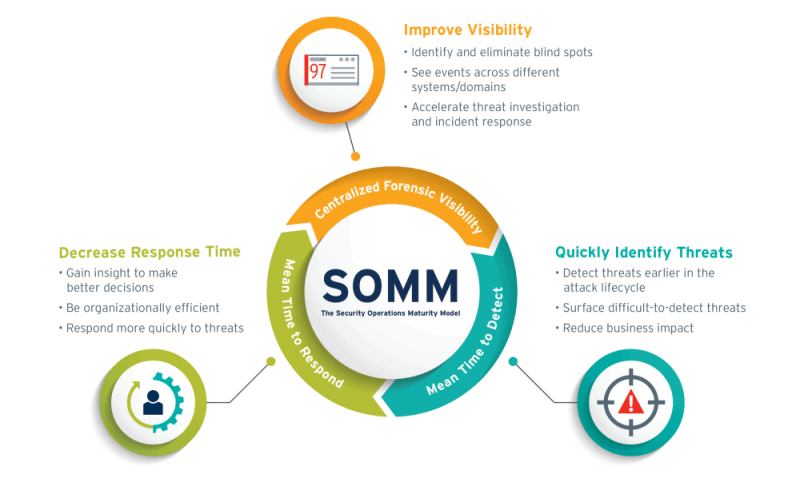
Move to the next-generation solution /SOMM/
First-generation SIEM solutions were limited in areas such as business and operational risk within IT environments and broad data filtering. Next-generation solutions improve team operations and results through automation and defined processes based on the needs of security teams. They manage highly efficient workflows, provide direct visibility into endpoints, deliver practical results, and continue to evolve to build a unified user database.
Блокын гарчиг / html
Easy and Secure Collaboration
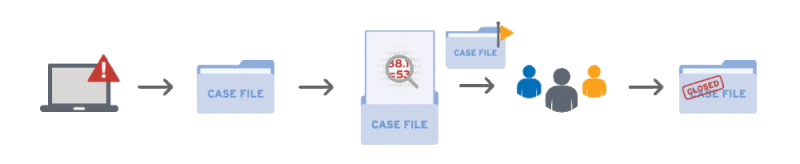
If your team has no central place to focus during an investigation, threats may enter through a gap. With Case Management, LogRhythm enables your team to create and track remediation activities during investigations. It also makes it easier for analysts to record time and assign tasks to team members.
XDR Stack
The LogRhythm XDR Stack architecture is a solution that combines the scale and flexibility your business needs. With XDR Stack, your organization can fully detect and respond to threats, putting log management and analytics, security analytics, security orchestration, automation, and response (SOAR) at analysts’ fingertips.
 LogRhythm AnalytiX centralizes your security and operational data and improves access to data from diverse logs and other devices.
LogRhythm DetectX precisely identifies malicious activity and threats, automatically connects with risk-protection tools, rapidly receives alerts, and enables quick response.
 LogRhythm RespondX, a security-orchestration, automation, and response (SOAR) solution, reduces team workload and lets analysts focus on what matters. By coordinating and automating as many detection and resolution steps as possible, RespondX simplifies threat investigation and mitigation.
 UEBA detects anomalous user behavior before data is compromised or exfiltrated.
 It detects emerging threats on rapidly changing networks and provides alerts to reduce risk to your organization.